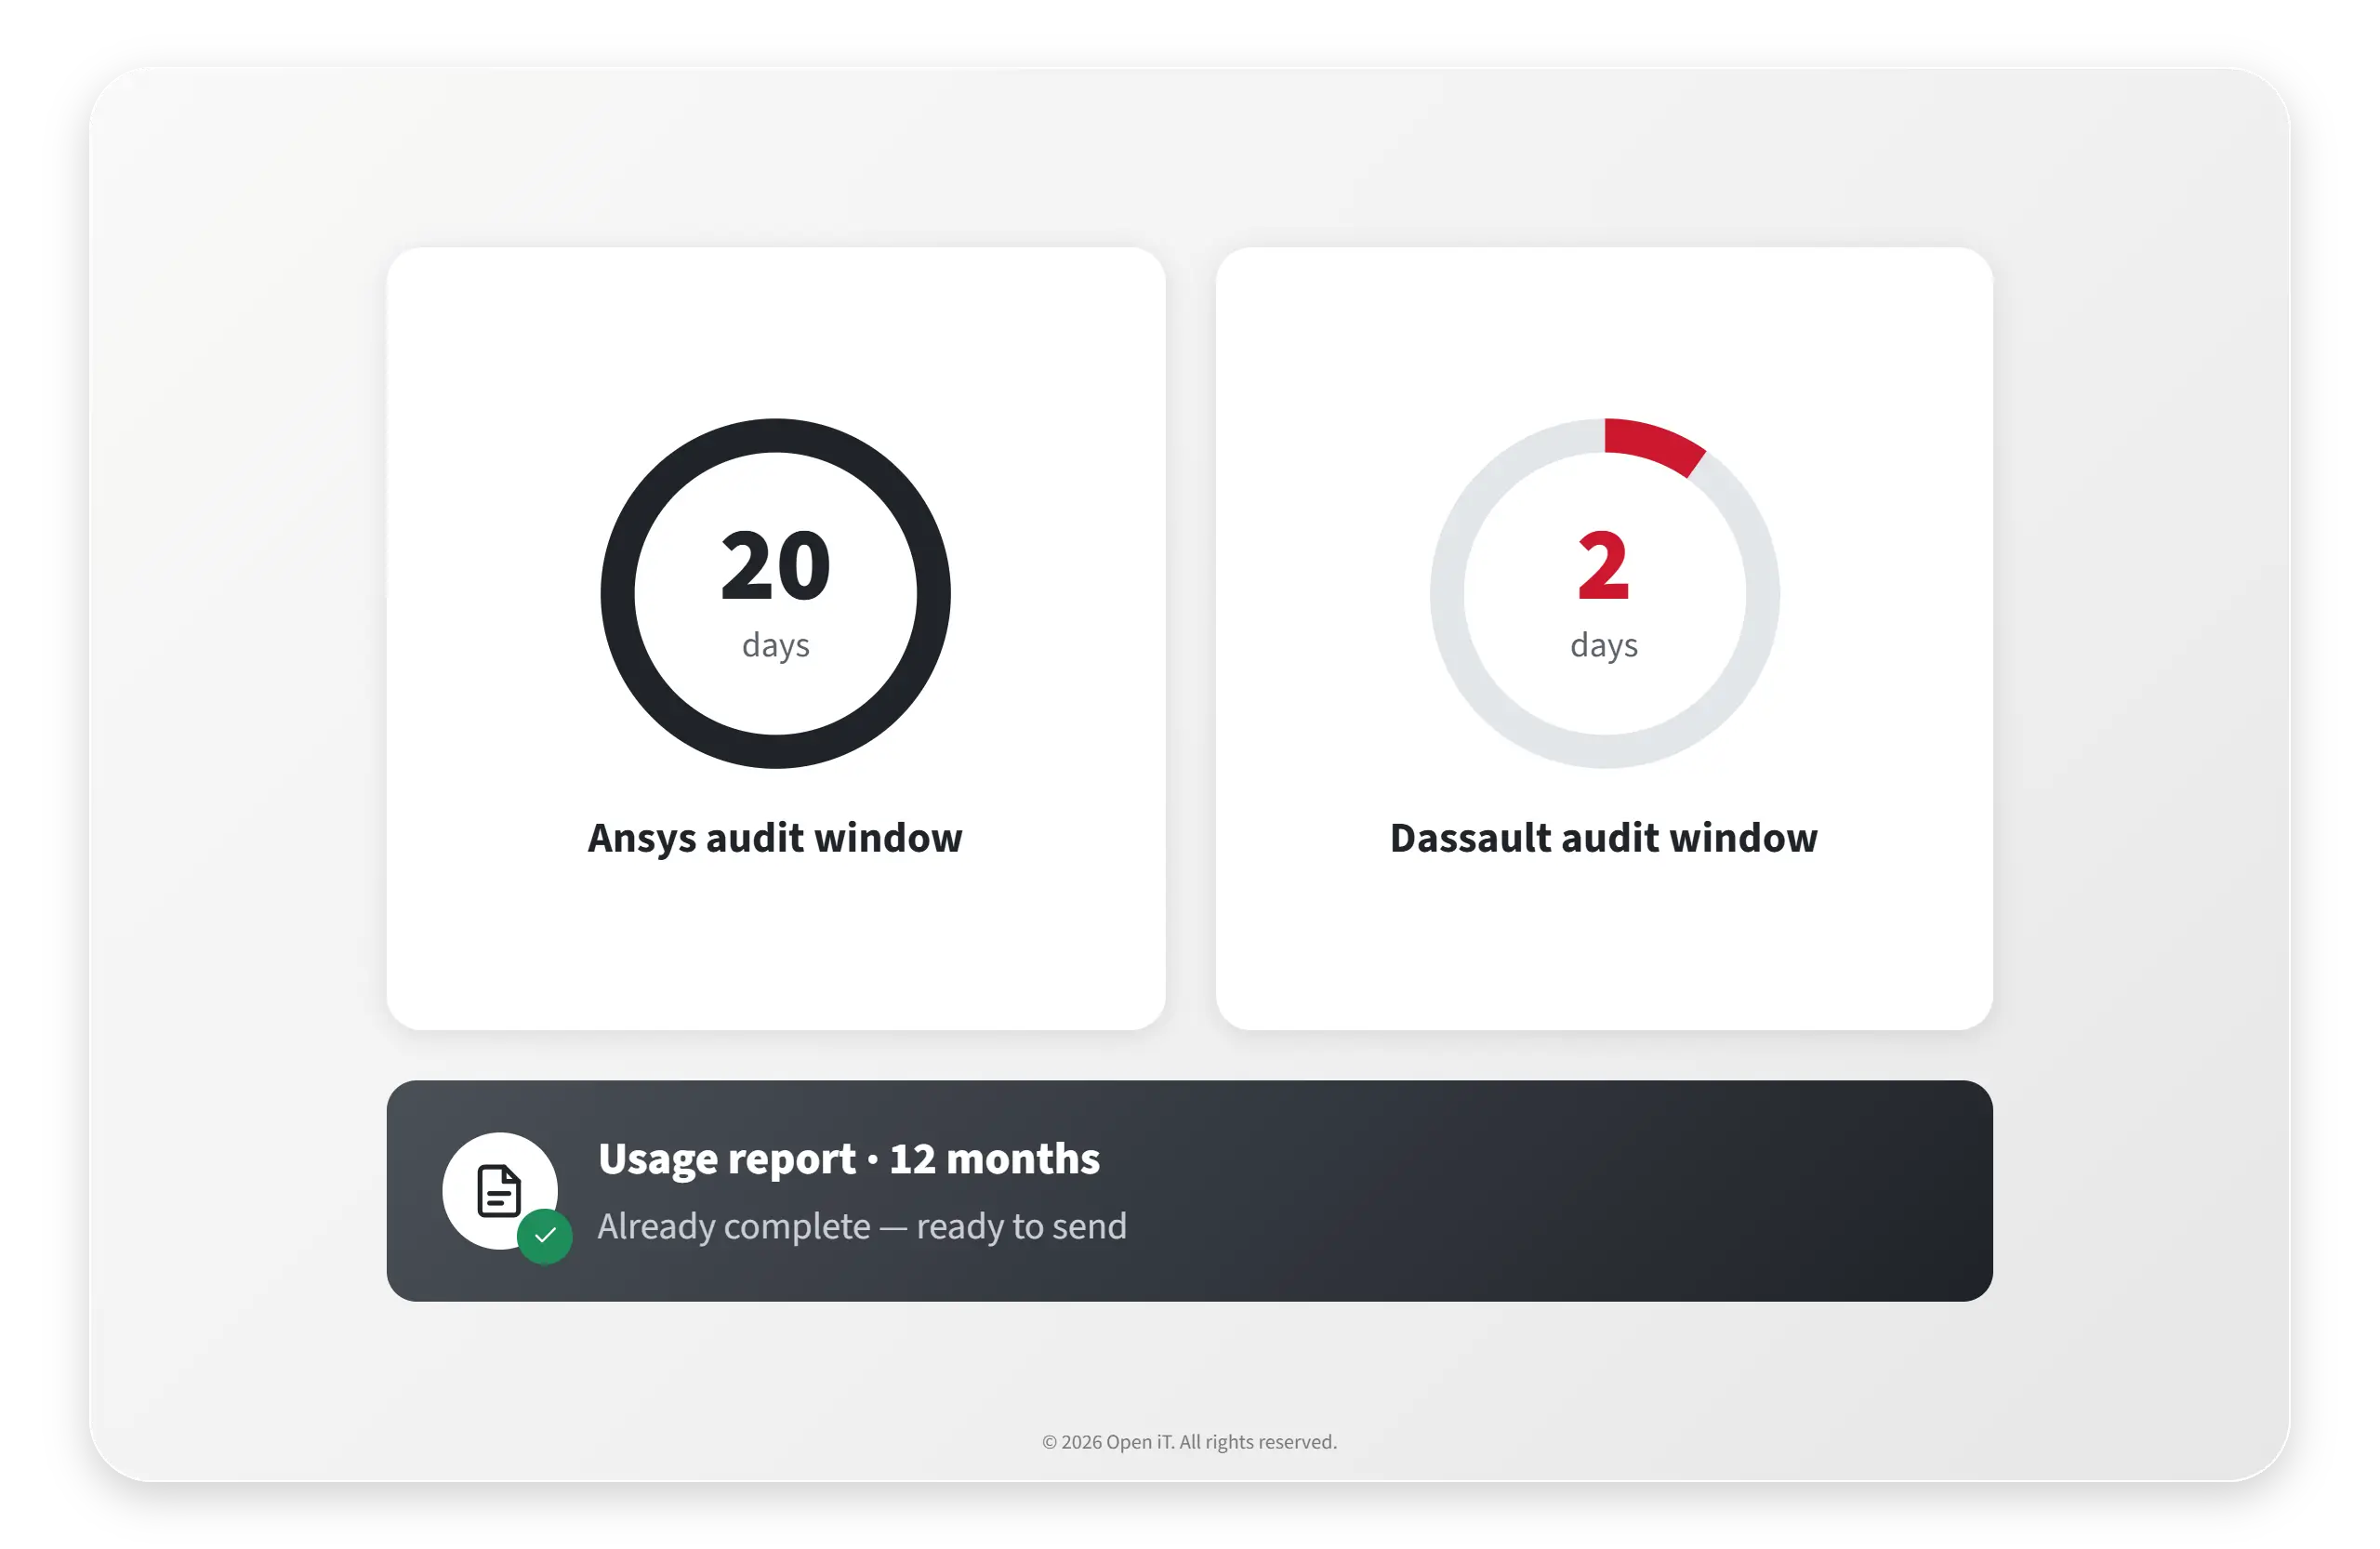
Ansys gives you twenty days. Dassault gives you two.
Open iT keeps the usage audit trail those clauses ask for, down to site, machine, time, date and hours per license, so an audit request is a report you run rather than a project you staff.
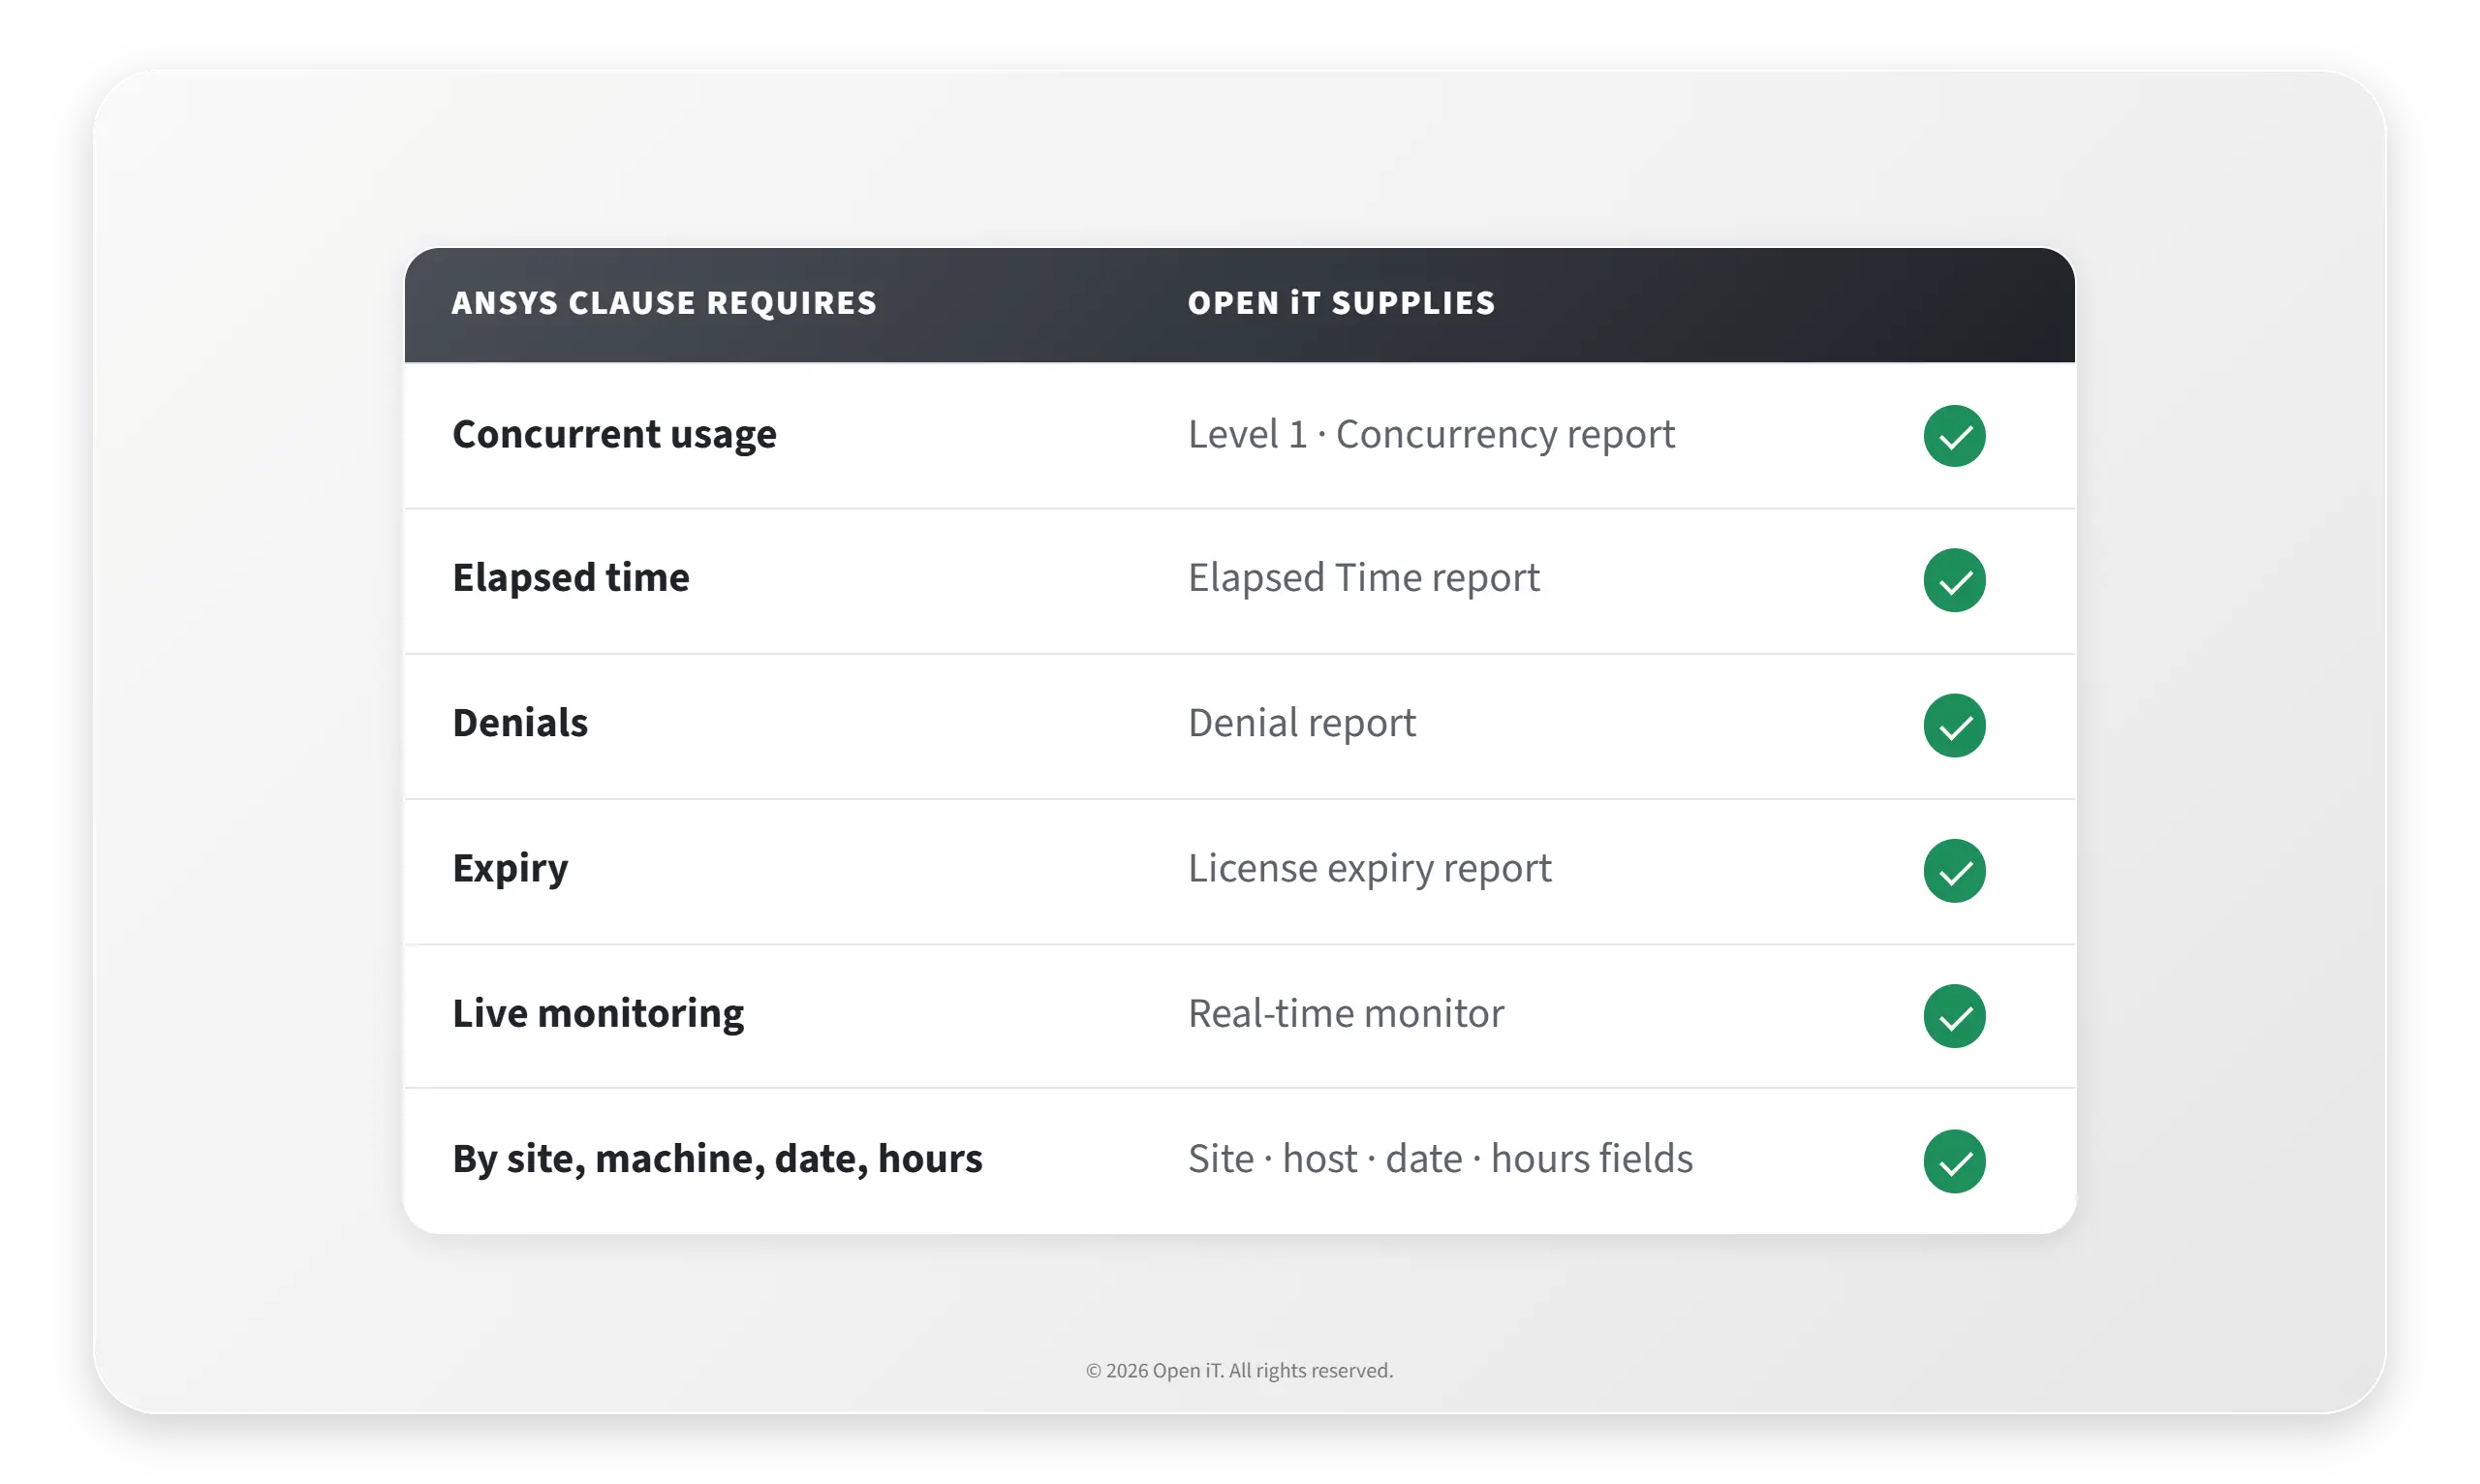
Ansys general terms call for a multi-site usage report drawn from the license manager: site locations, machine identifiers, time, date and hours of access per license, within twenty days of a request. Notice runs to fifteen days, once a year. Where an audit finds unlicensed use, the terms provide for list price plus damages payable within thirty days. Dassault runs tighter still: records within three business days, machine access with audit-tool execution within two, and a shortfall above five percent shifts the cost of the audit onto you.
Most estates start assembling that evidence after the letter arrives. That’s where the twenty days go, and it’s why the answer that goes back is usually incomplete, which is the worst position to argue from.
Was Open iT leistet
1
Keep the trail before you need it.
Level 1 maintains a usage audit trail for compliance and historical review across your license servers. The record is already there when the request lands, covering the period the vendor asks about rather than the period you started logging.
2
Report what the clause actually asks for.
Concurrent usage, elapsed time, denials, expiry and live monitoring come out of Level 1, broken out by site, machine, date and hours. That’s the shape of report the Ansys clause describes, which makes the response an export rather than a reconstruction.
3
Send the usage without sending your people.
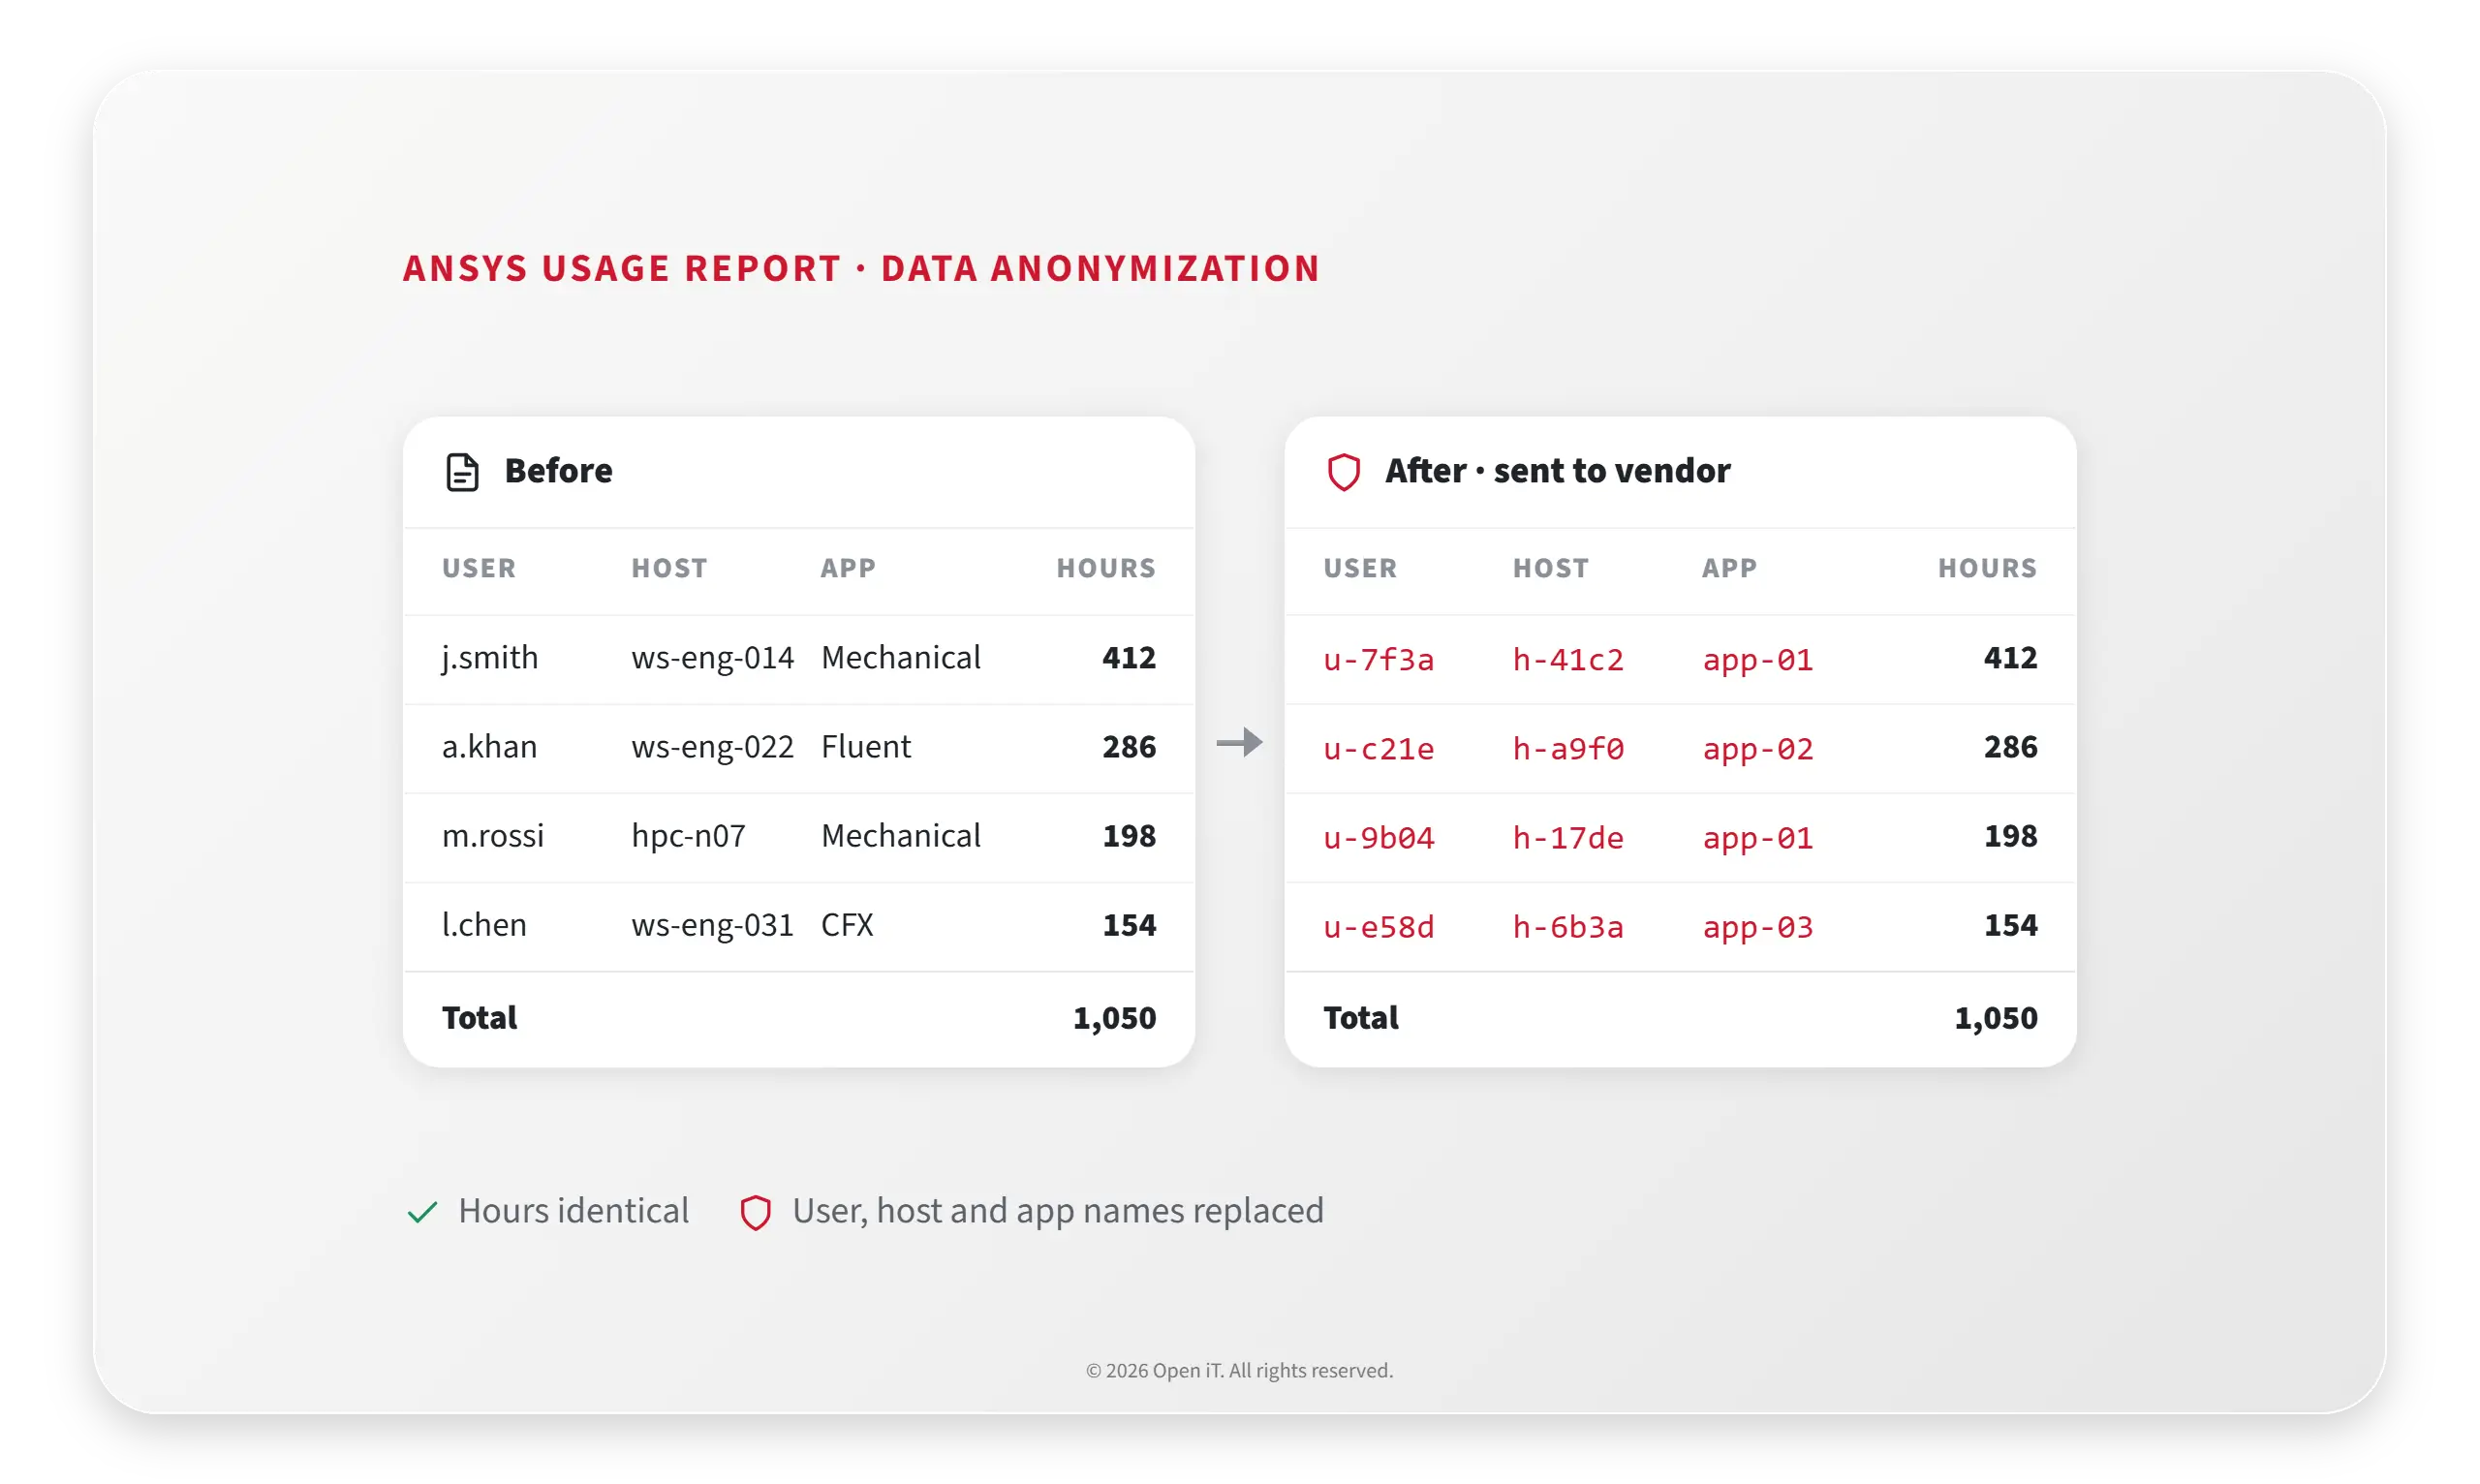
Ansys’s own terms state the customer isn’t obligated to include personal information in the report. Data Anonymization transforms user, host and application names while keeping the usage data reliable, so you meet the obligation in full and still hand over nothing about individuals.
4
Show the license-management history too.
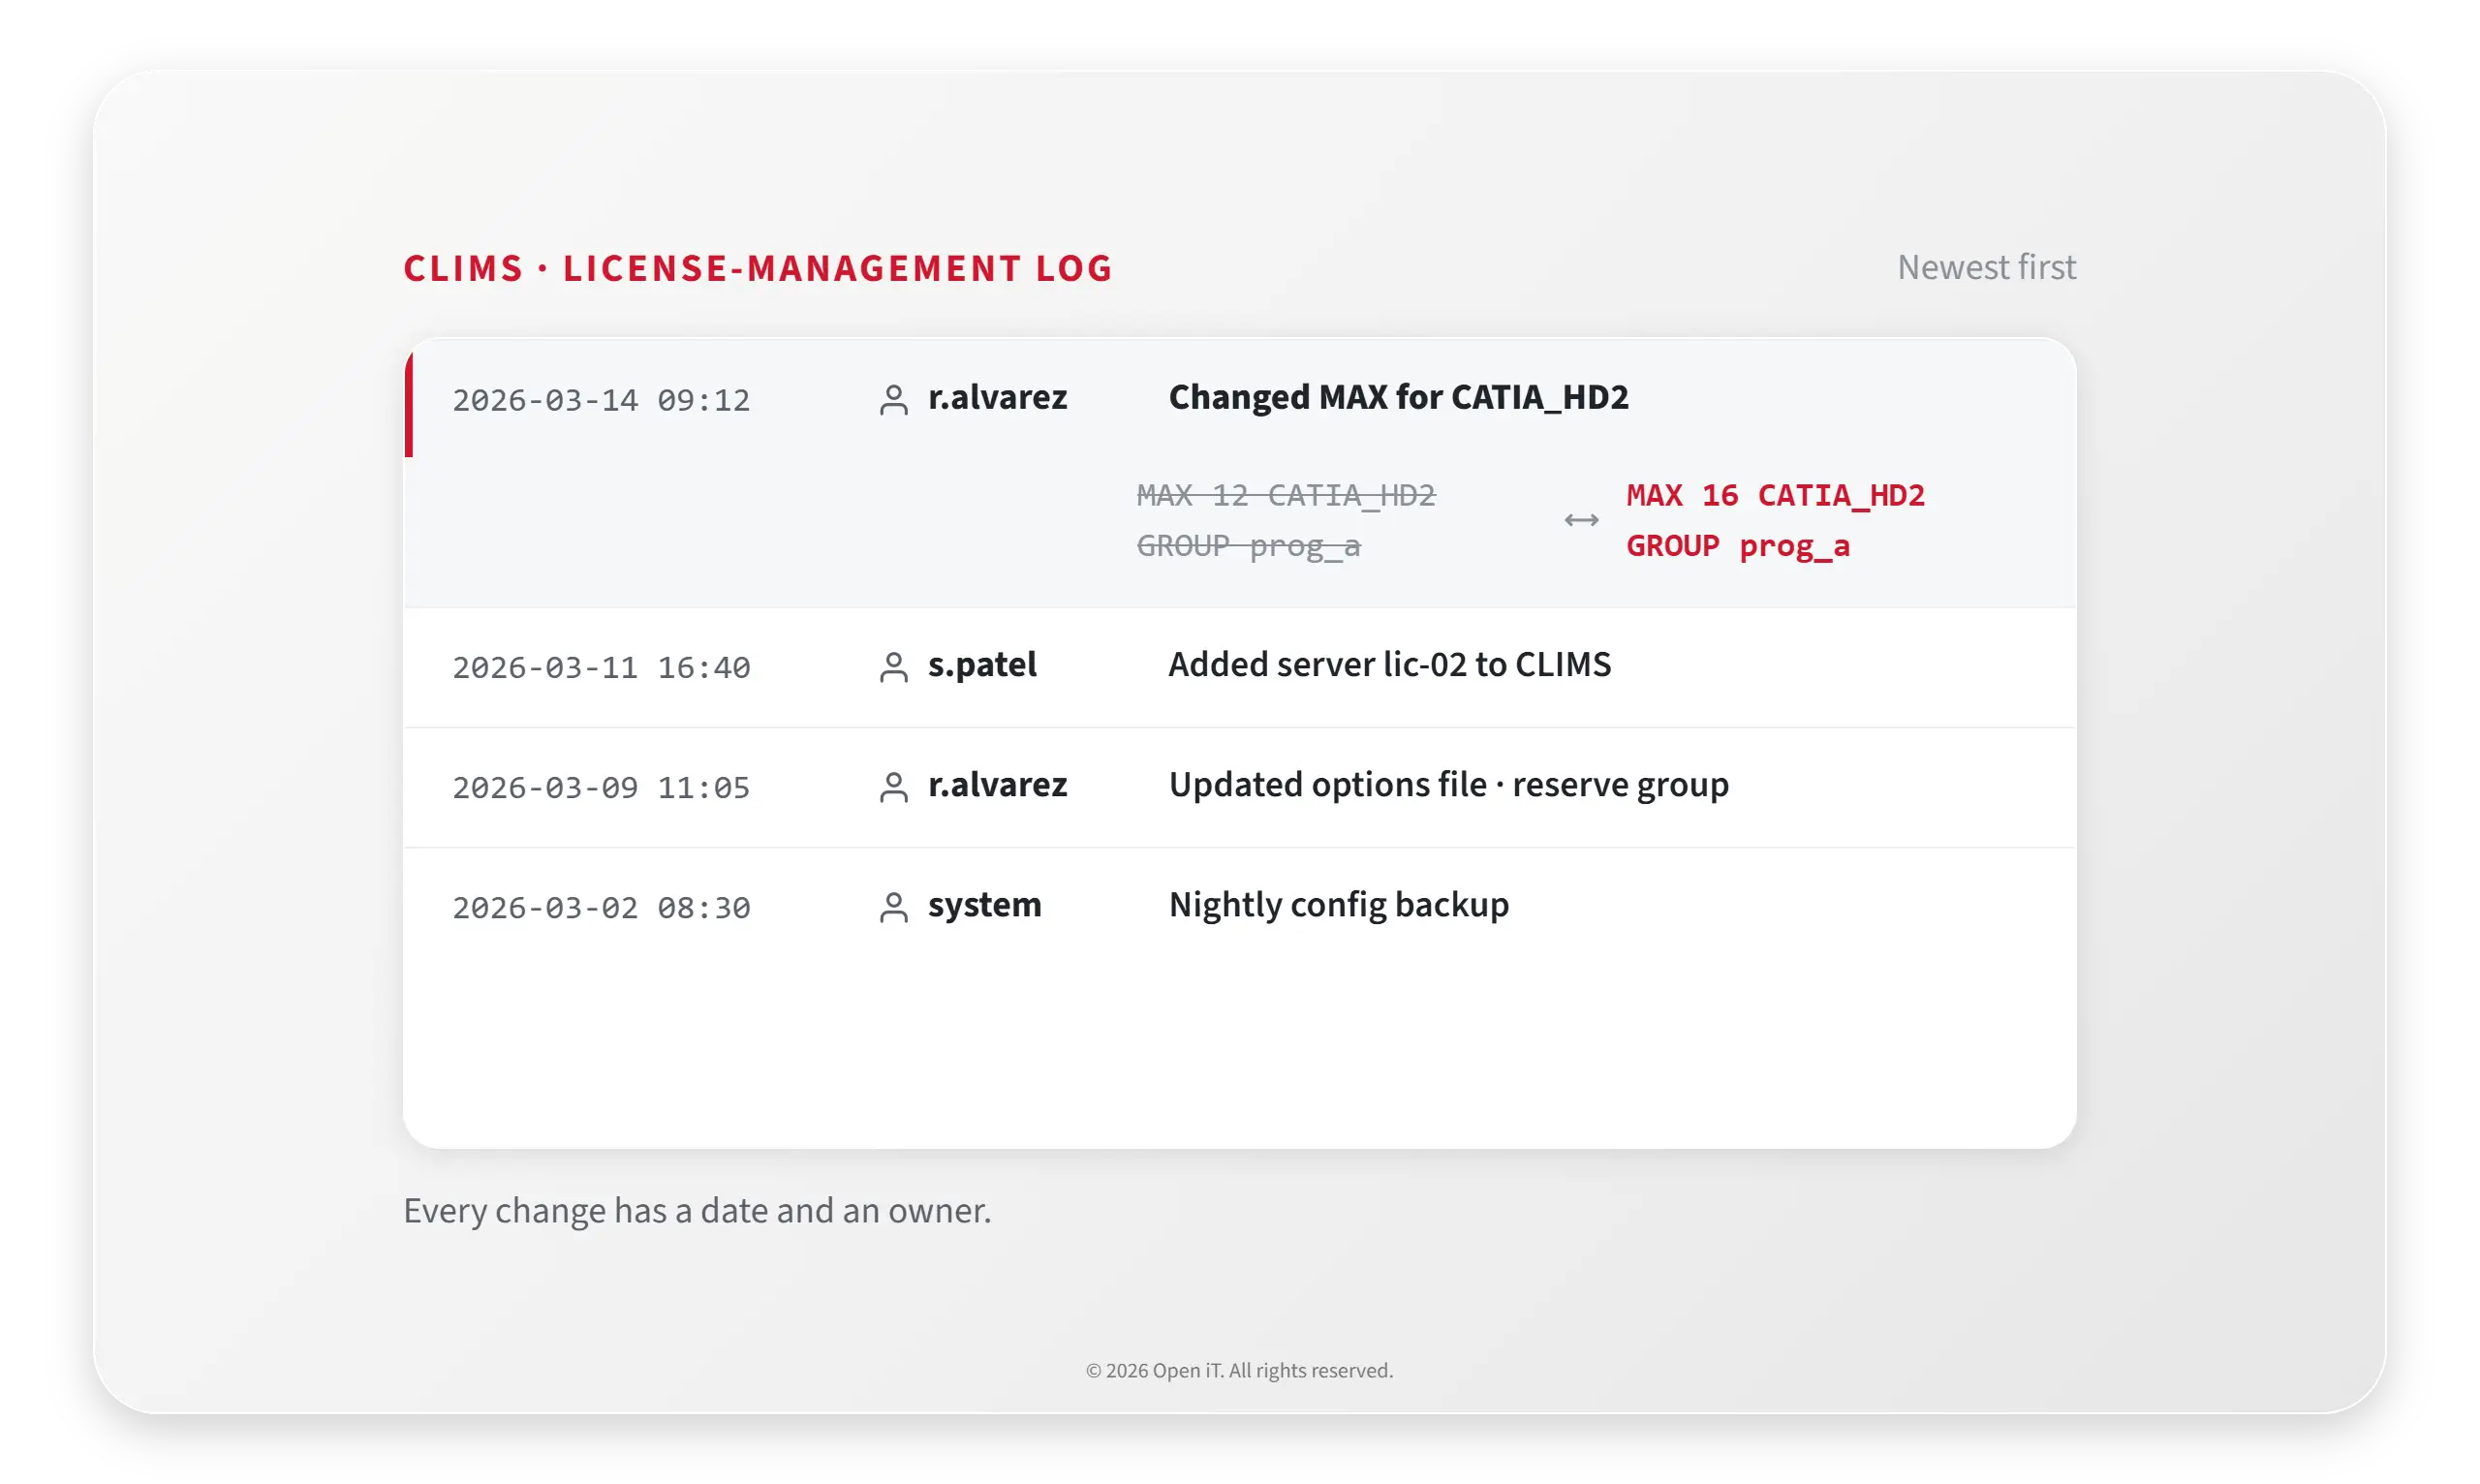
CLIMS logs every license-management action. The product documentation names aerospace and defense among the regulated industries that trail exists for. When a vendor questions a configuration change, the change has a date and an owner.
Haben Sie Fragen? Wenden Sie sich an einen Lizenzspezialisten.
Answer eight questions and see whether you could meet a twenty-day Ansys request and a three-day Dassault one from what you hold today.
From the day a request arrives to the day you can send it.
0 of 7
audit-readiness capabilities in place
Ansys request (20-day window)
–
Dassault request (3-day window)
–
Days you need to produce a report
–
How this is scored
Seven of the eight questions describe what you hold today. Each earns a point if the answer is fully yes, half a point if it is partly true, and nothing if not. The eighth, days needed to produce a report, is checked against each request window.
Points: a standing audit trail, export by site and machine, anonymization on export, 12 months or more of history (half a point for 6 to 12 months), coverage of every license server (half a point for most), who held a license and for how long, and continuous collection (half a point for a schedule).
Ready: you can produce the report inside the window, you have a standing audit trail, and you score at least 6 of 7.
At risk: you can meet the window, but the record has gaps.
Not ready: you need more days than the window allows, or there is no standing audit trail.
This scorecard compares your record against a 20-day window for an Ansys request and a 3-day window for a Dassault one. Check the window in your own agreement, since it is the one that applies to you.
For planning discussion only. The result is based on the answers you gave, not on a review of your records.
Häufig gestellte Fragen
How fast can we produce a usage report?
As fast as you can run an export, because the trail is already collected. Level 1 keeps a usage audit trail across your license servers, so a request covering the last twelve months is answered from data you hold rather than from logs you have to assemble.
Do we have to hand over usernames?
Ansys’s terms state the customer isn’t obligated to include personal information in the report. Data Anonymization transforms user, host and application names while keeping the usage figures intact, so the report is complete and the people in it aren’t identified.
Do denial records count against us in an audit?
A denial means somebody was refused a license, which is evidence of a shortage rather than of unlicensed use. It’s more often useful at the renewal than risky at the audit.
Does this replace our software asset management platform?
No. Open iT meters what gets used. Your software asset management platform holds what you own: purchase orders, entitlement records, allocation workflows. Both join through the ServiceNow integration and SSAD normalization.
The clause is already in your agreement and the clock is already set. The only variable left is whether the report exists before the letter does.